GitLab BlogGitHub
Dependency Firewall: Block risky packages before the build
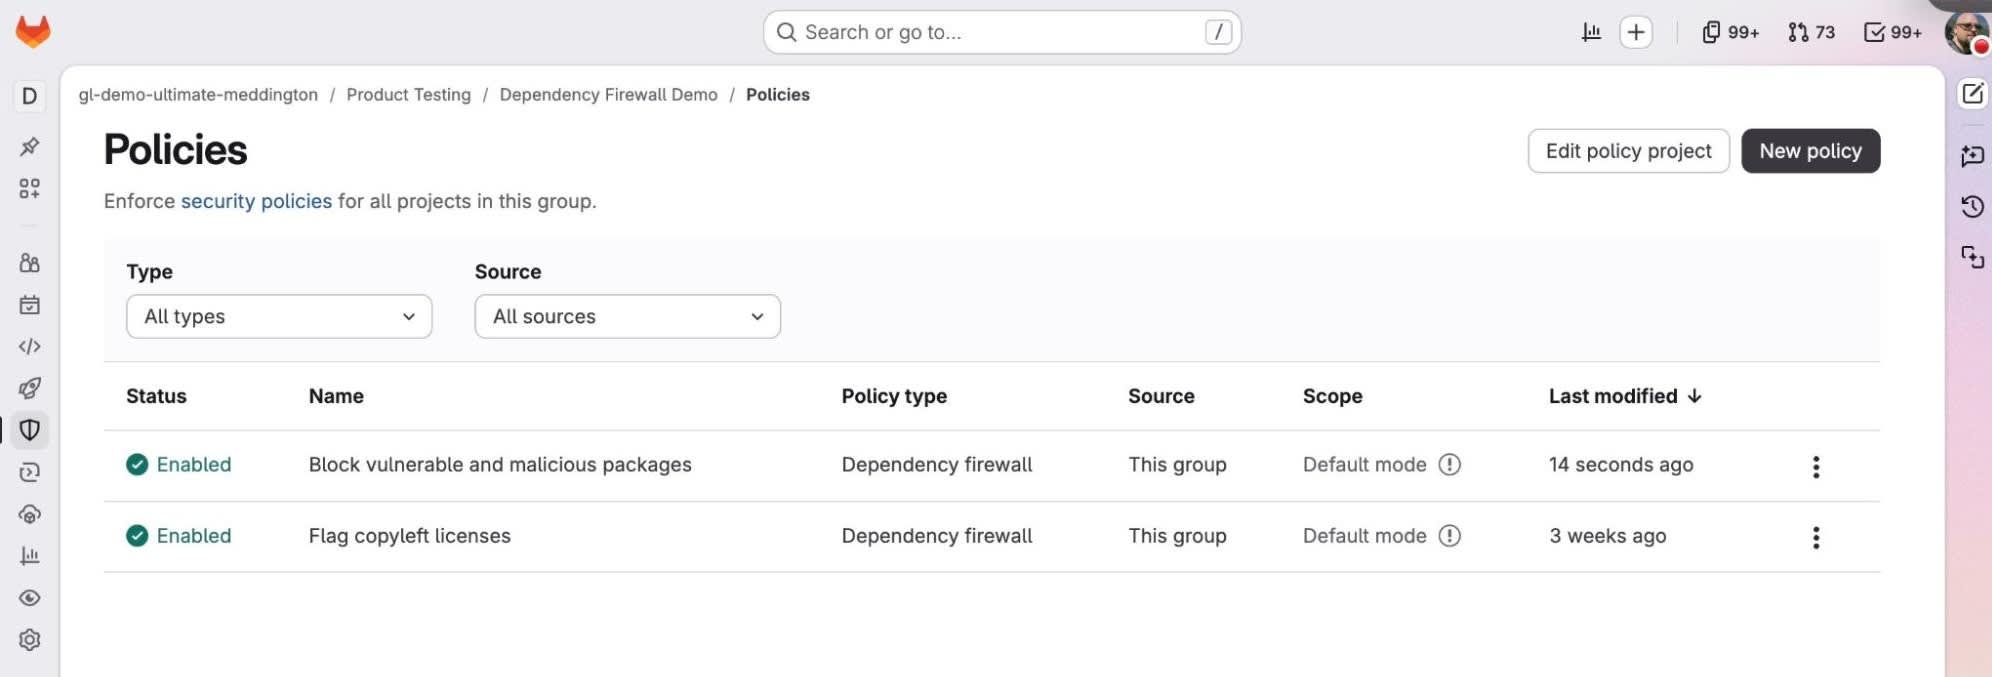
Attackers disguise malicious packages as ones you trust. In June 2026, GitLab researchers found five malicious PyPI packages , four of them typosquats of Flask, Requests, and NumPy, that run at…
Read at GitLab Blog ↗More from GitLab Blog on Accept All
GitHubGitLab Transcend: Speed you can trust, all the way to production GitLab Blog
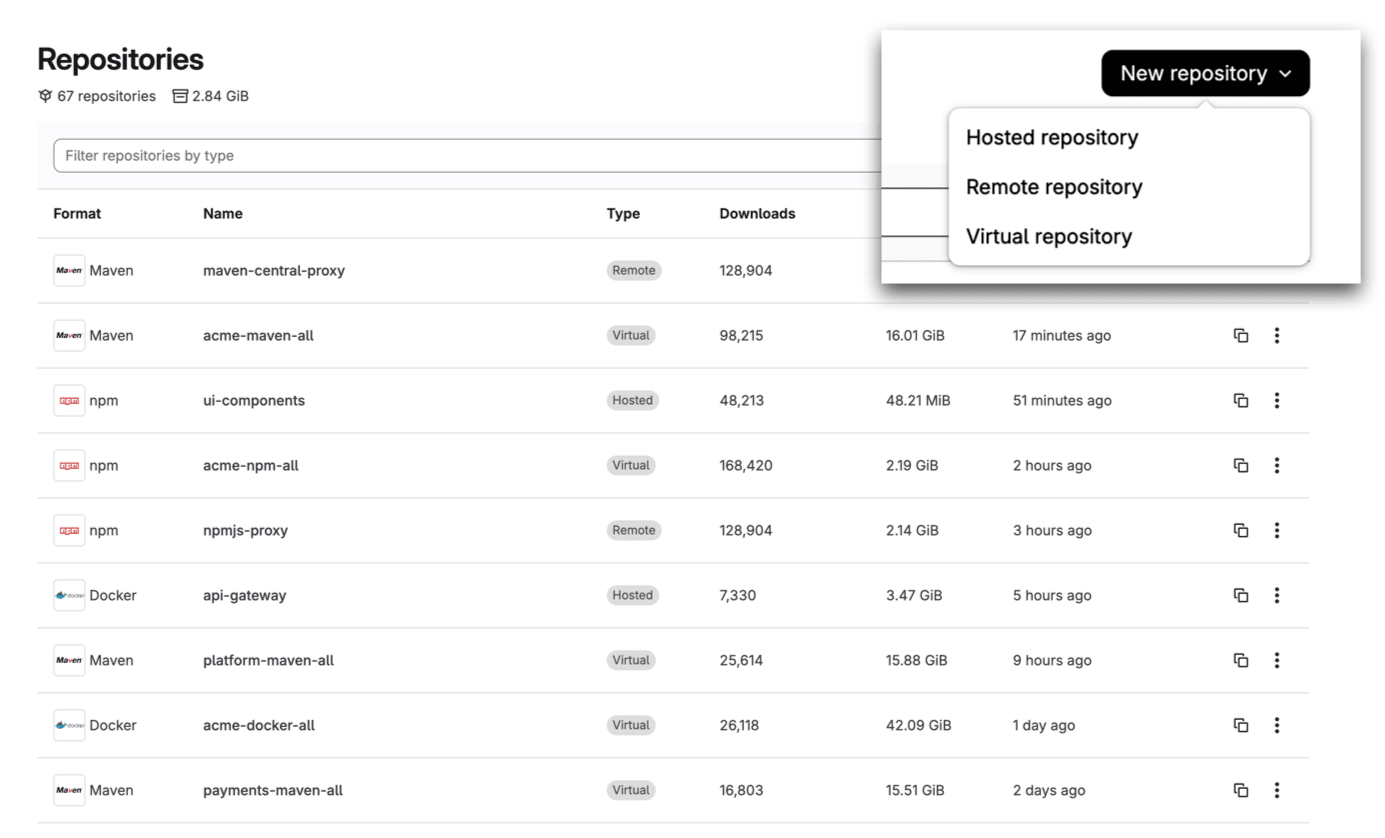
GitHubEvery artifact your teams ship, assembled right the first time GitLab Blog

GitHubTwo front doors: Module-level access in a Django GRC app GitLab Blog